
Secure decisions before risk becomes exposure.
A semantic intelligence layer 鈥� not another cyber dashboard.
Mission-relevant security intelligence requires closing three gaps.
Crypto Inventory Blind Spots
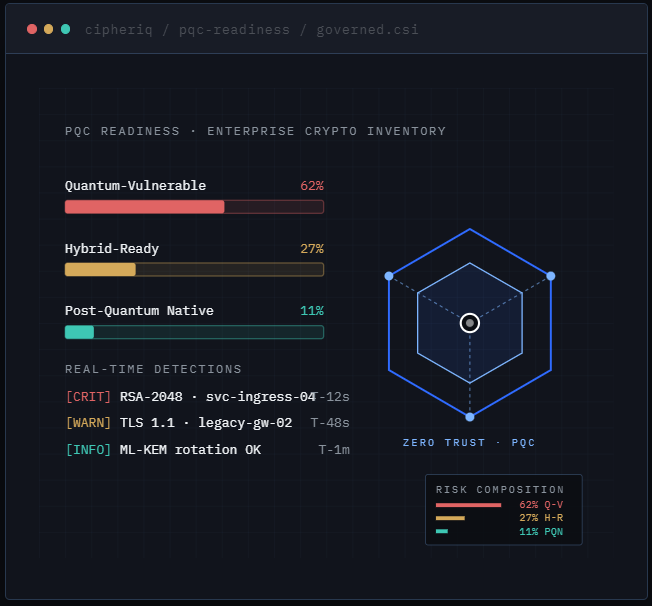
Most enterprises don't know where their cryptography lives 鈥� which algorithms, which key sizes, which protocols, which services. CipherIQ continuously discovers and inventories cryptographic assets across systems, services, and traffic, producing a governed map operators can actually act on.
Post-Quantum Migration
Migrating to post-quantum cryptography requires sequencing across decades-old systems, vendor dependencies, and risk-weighted priorities. CipherIQ surfaces PQC exposure by asset, scores migration readiness, and tracks remediation progress 鈥� turning a vague mandate into a structured, auditable program.
Adaptive Defense at Scale
Threats evolve faster than annual reviews. CipherIQ pairs AI analytics operating at a configured processing cadence with cryptographic context so defensive policy can adapt as risk signals shift 鈥� with explicit provenance on every detection, decision, and remediation action.
What CipherIQ does today.
Cryptographic Inventory Coverage
Discovers and inventories cryptographic assets across the systems, services and network traffic included in the approved assessment scope. Coverage is measured against that defined boundary, with source provenance and refresh timestamps attached to each record.
PQC Readiness Tiers
Quantum-vulnerable, hybrid-ready, post-quantum-native 鈥� every cryptographic asset scored against published NIST PQC standards with explicit migration priority.
AI Analytics
Threat-context analytics over live cryptographic telemetry. Every detection carries source attribution, model version, and confidence band 鈥� audit-ready by default.
Deployment Configurations
Software, Dell-compatible appliance, edge, on-prem, secure customer-controlled environment, multi-node enterprise. CipherIQ fits the security architecture, not the other way around.
Honest Bounds 鈥� What's Still in Scope
Automated remediation across third-party vendor surfaces, real-time PQC algorithm substitution in production traffic, and cross-domain trust federation at hyperscale remain active development scope. CipherIQ is presented as a credible, available for a scoped pilot, security intelligence layer 鈥� with bounded activation, processing, and sustainment packs designed to grow alongside customer security posture, not as a finished platform that pretends every capability is mature.
From cryptographic sprawl to governed security intelligence.
- Crypto asset inventory across systems, services, and traffic 鈥� with every entry carrying explicit source attribution and refresh history.
- Post-quantum migration planning sized to actual exposure, vendor dependencies, and risk-weighted priorities.
- Adaptive defense that pairs AI analytics operating at a configured processing cadence with cryptographic context, with policy changes audited end-to-end.
- Regulatory compliance & audit-readiness with provenance and tier badges carried through every detection and remediation.
- Mission resilience in federal, defense, and intelligence environments 鈥� deployable as appliance, edge, on-prem, or air-gapped configuration.
Today, conditional, and roadmap.
Software, appliance, & edge deployment
Aperio software deployment, Dell infrastructure configuration under validation configuration, edge, on-prem, secure customer-controlled environments, and multi-node enterprise architectures. Can be scoped through 探花视频鈥檚 quote pathway.
SIEM / EDR / identity integration
Bidirectional integration with existing SIEM, EDR, and identity tooling so CipherIQ adds cryptographic context to the SOC's existing decision surface. Subject to vendor connector scope.
Automated PQC remediation
Programmatic substitution of quantum-vulnerable algorithms with NIST-standard PQC equivalents, sequenced by risk-weighted priority. Planned post-pilot once base cryptographic visibility is validated at customer scale.