
Secure AI Adoption for Agencies
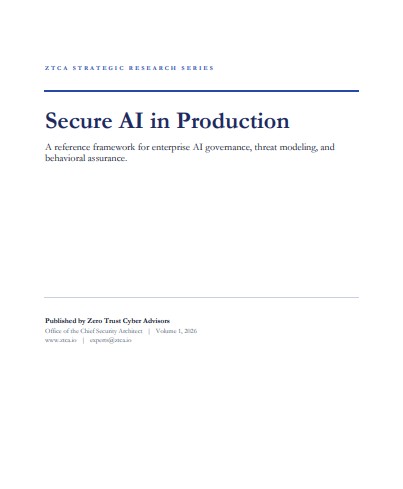
Deploying Microsoft Copilot introduces powerful new capabilities—but it also brings a unique set of security and governance challenges that organizations must address before rolling it out at scale. This resource provides a clear, practical walkthrough of the risks associated with Copilot, including data oversharing, prompt injection, permission misuse, AI hallucinations, and exposure through third鈥憄arty plugins. It outlines a Copilot鈥憇pecific threat model, a secure deployment architecture, and a phased approach that spans assessment, remediation, deployment, and continuous monitoring. You’ll also learn how Zero Trust principles and established frameworks from NIST and CISA can be applied to ensure secure, compliant AI adoption across the enterprise.
Key bullets to encourage access:
-
Understand the unique security and governance risks introduced by Microsoft Copilot
-
Explore a Copilot鈥憇pecific threat model and secure deployment architecture
-
Follow a phased approach for assessment, remediation, deployment, and ongoing monitoring
-
Learn how Zero Trust principles strengthen Copilot security and data protection
-
See how NIST and CISA frameworks support compliant, enterprise鈥慻rade AI adoption
-
Gain practical guidance for reducing risk while enabling responsible AI use at scale